Agent-Only Security Roles: The D365 F&O Skill to Learn Now
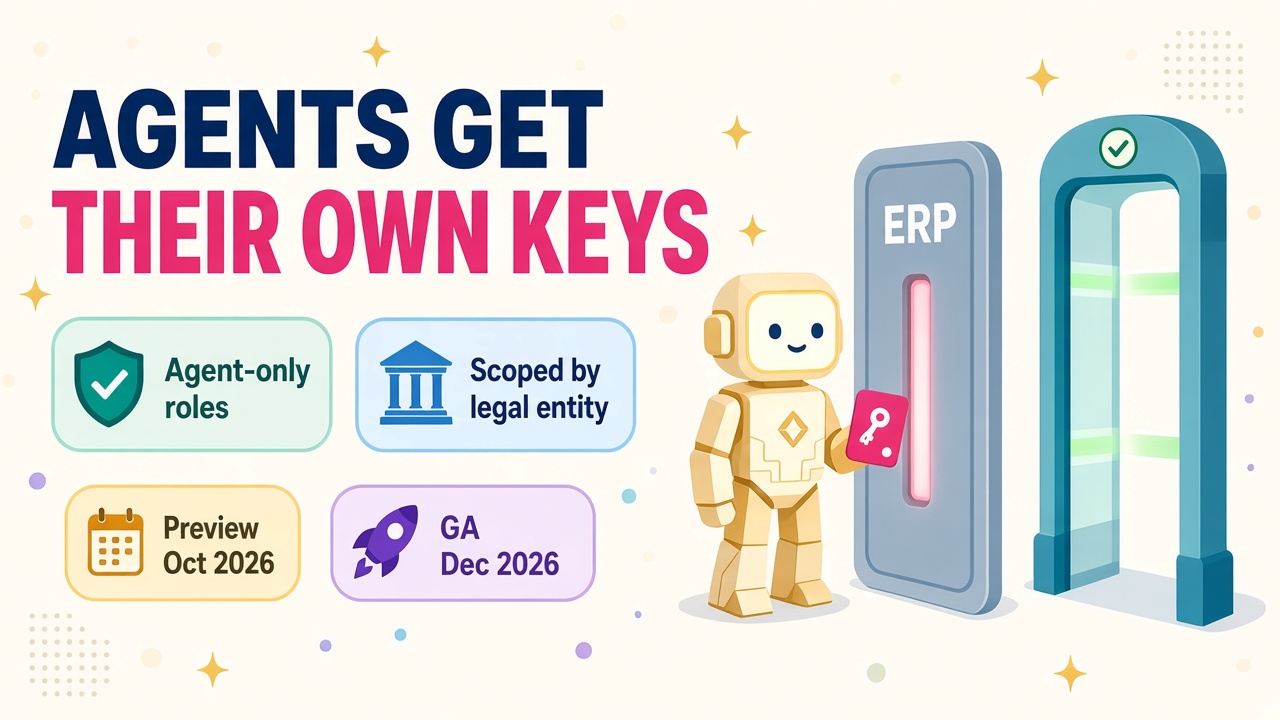
Microsoft is giving D365 F&O agents their own narrower security roles, scoped by legal entity. Preview now, GA in December. Here is how to get ahead of it.
If you work anywhere near Dynamics 365 Finance and Operations security, a small roadmap item from October deserves a big circle on your calendar. Microsoft is giving ERP agents their own security restrictions, separate from the person they act for. Preview started in October 2026 and general availability is pencilled in for December 2026.
It sounds like admin plumbing. It is actually the thing that decides whether finance teams let agents anywhere near the ledger, and that makes it one of the most useful skills a D365 consultant can pick up before Christmas.
What has Microsoft actually announced?
The feature is roadmap item 571677, "Role-based access controls for ERP agents", posted on 1 October 2026. In Microsoft's words, ERP security administrators can apply additional, agent-specific restrictions that take effect when a user accesses the ERP through an agent.
The clever bit is that there is no new security model to learn from scratch. Administrators use the roles, duties and privileges they already maintain, assign them so they apply only to agent-initiated requests, and scope them by legal entity. The result is that a user's agent session can run with narrower permissions than the same user has when they log in and click around themselves.
The quick facts:
- Release phase: preview from October 2026, general availability planned for December 2026.
- Clouds: Worldwide commercial, GCC and GCC High.
- Building blocks: existing roles, duties and privileges, applied only to agent requests.
- Scope: by legal entity, so an agent can be trusted in one company and kept out of another.
Why does this matter so much?
Until now the rule has been simple. The Microsoft Learn page on ERP MCP security is clear that the Dynamics 365 ERP MCP server never elevates privilege. A user working through an agent can never do more than they could in the normal client, because every request runs under that user's roles, duties, privileges, record-level security and data security policies.
That is reassuring, but it only goes one way. It stops an agent doing more than the user. It doesn't let you say "my financial controller can post journals, but I don't want her agent posting journals at 2am on her behalf".
Anyone who has sat in a finance steering committee knows that is exactly the question that comes up. A controller with broad access is fine because she is a careful human with a reputation and a mortgage. An agent with the same access is a different risk conversation, even if it is brilliant at the job. Agent-only restrictions answer that question with tools auditors already understand.
I am quite certain this is what unlocks the next wave of agent rollouts in F&O. Microsoft's September agentic ERP roadmap is full of agents that touch money and stock: the Account Reconciliation Agent, Finance Agent skills for reconciliation and collections, and the Procurement Agent's impact analysis on supplier purchase order changes. Every one of those projects will hit the same security review. The people who can design the answer will be busy.
How does agent security work in F&O today?
It helps to understand the full stack, because agent-only roles sit on top of things that already exist.
Identity comes first
Microsoft Learn describes two patterns. For chat or delegated agents, the agent runs on behalf of the user who is chatting with it, so actions are attributable to that person. For autonomous agents there is no human in the chat, so the agent has its own identity and that identity is the authenticated user.
The agent deployment wizard guidance spells out what that means in practice: each agent runs under a dedicated agent user identity, created in the Microsoft 365 admin centre if needed, licensed, added to the Dataverse environment with Dataverse roles, and then added to the finance and operations environment with the relevant F&O security roles.
Then control which clients can connect
The ERP MCP server has an Allowed MCP clients form. By default it lets in Microsoft Copilot Studio, Visual Studio Code, Microsoft Cowork and the Finance Agent. Anything else has to be registered as an application in Microsoft Entra ID and added to that form with Allowed set to true. That is a genuine control point, and plenty of environments will want it locked down tighter than "whatever a developer added last Tuesday".
Business logic still applies
The MCP server isn't a back door into the database. It goes through standard F&O APIs such as OData endpoints and custom services, so validations, workflows and server-side rules run as normal. If a transaction would be rejected in the client, it is rejected through the agent too.
And now, agent-only restrictions
Agent-only roles add the missing layer: a deliberately narrower slice of access that applies only when the request comes through an agent. Same roles, duties and privileges, different context.
What will a good agent security design look like?
The feature is still in preview and Microsoft hasn't published every detail, so test in a sandbox before promising anything to a client. But the design thinking doesn't need to wait. Here is how I would approach it.
- Start from standard roles. Microsoft ships around 100 standard security roles in F&O with segregation of duties built in, and its own implementation guidance says to duplicate and modify them rather than build from scratch. Do the same for agent roles.
- Write each agent's job description. Before touching a privilege, write one paragraph on what the agent should do. "Match supplier confirmations to purchase orders and flag changes" needs read access to POs and vendor data, not the right to approve invoices.
- Default to read, add write deliberately. Most early agent value comes from finding, summarising and preparing. Give write privileges only where a person reviews the outcome, which is the pattern Microsoft's own previews follow.
- Use legal entity scoping. Pilot an agent in one company, prove it, then widen it. That is a much easier conversation with a group CFO than a big bang.
- Keep segregation of duties intact. If a human can't both create a vendor and pay them, an agent acting for that human shouldn't either. Check your SoD rules against agent roles explicitly.
- Lock the client list. Review the Allowed MCP clients form as part of every go-live checklist.
- Check where data goes. Microsoft notes the MCP server doesn't store customer data, but retention outside F&O depends on the agent client, whether that is Copilot Studio, Claude or Microsoft Foundry. Data handling belongs in the design document.
- Review agent instructions. Microsoft's own admin guidance says to check agent instructions don't encourage users to attempt actions outside their responsibilities. Treat prompts as part of the security design, not an afterthought.
Who should learn this?
Pretty much everyone on an F&O project will brush up against it, but some roles get the biggest lift.
F&O security and compliance consultants
This is your moment. You already know roles, duties, privileges and XDS policies inside out. Adding agent-only restrictions to your toolkit turns you into the person who signs off agent rollouts. Expect project scopes to include an "agent security design" workstream as these features land.
Technical and solution architects
Architects will need to explain identity patterns, client allow-lists and data handling to customer IT and risk teams. Being fluent in the difference between delegated and autonomous agents is now table stakes.
Functional finance and supply chain consultants
You don't need to configure privileges yourself, but you do need to describe what an agent should and shouldn't touch in your process area. The consultant who turns "let the agent chase suppliers" into a precise access brief saves everyone a week of rework.
Internal auditors and risk specialists
Auditors who understand agent access are going to be in short supply. If you sit on the customer side, learning this now means you shape the controls rather than inherit them.
What should you do this month?
Plenty of this can be done in a sandbox over a few evenings.
- Read the Microsoft Learn MCP security page end to end. It is short and it explains the model clearly.
- Spin up or borrow a tier-one sandbox and look for the agent security feature in your version. If it isn't there yet, practise the identity steps in the agent deployment wizard instead.
- Map one real agent. Take the Procurement Agent or Account Reconciliation Agent, write its job description and draft the narrowest role that would let it work.
- Build an SoD check. List the segregation of duties rules your customers care about and test whether an agent role could break any of them.
- Write a one-page explainer for a finance director on delegated versus autonomous agents. If you can explain it simply, you can sell the work.
- Watch Microsoft Ignite, 17 to 20 November. Microsoft has signalled more agentic ERP news, and agent security is likely to come up again.
Is this good news for D365 careers?
Very much so. Every time Microsoft adds a serious control, it gives cautious customers a reason to say yes. Finance teams have been curious about agents but nervous about access, and nervousness costs projects. Agent-only roles turn "we're not sure" into "show us the design", and someone has to produce that design.
It also widens the field. Security in F&O has often been a niche specialism handled late in a project. With agents acting on the ledger, it moves to the front of the plan, which means more early involvement, more visibility and, in my view, better rates for the people who are good at it.
The exponential age needs guardrails as much as it needs clever agents. The consultants who build those guardrails will have very full diaries in 2027.
What to do next
- Browse D365 jobs and look for F&O security, compliance and architect roles mentioning Copilot or agents.
- Check D365 salaries to see what security and architecture specialists are earning.
- Add agent security design to your profile on our consultants directory so employers can find you.
- Hiring? Post your role on our employers page and say clearly that agent security is in scope.
- Explore partner tools on our products and vendors pages that help with F&O security reviews.